
Ahmedabad. 15 September 2026
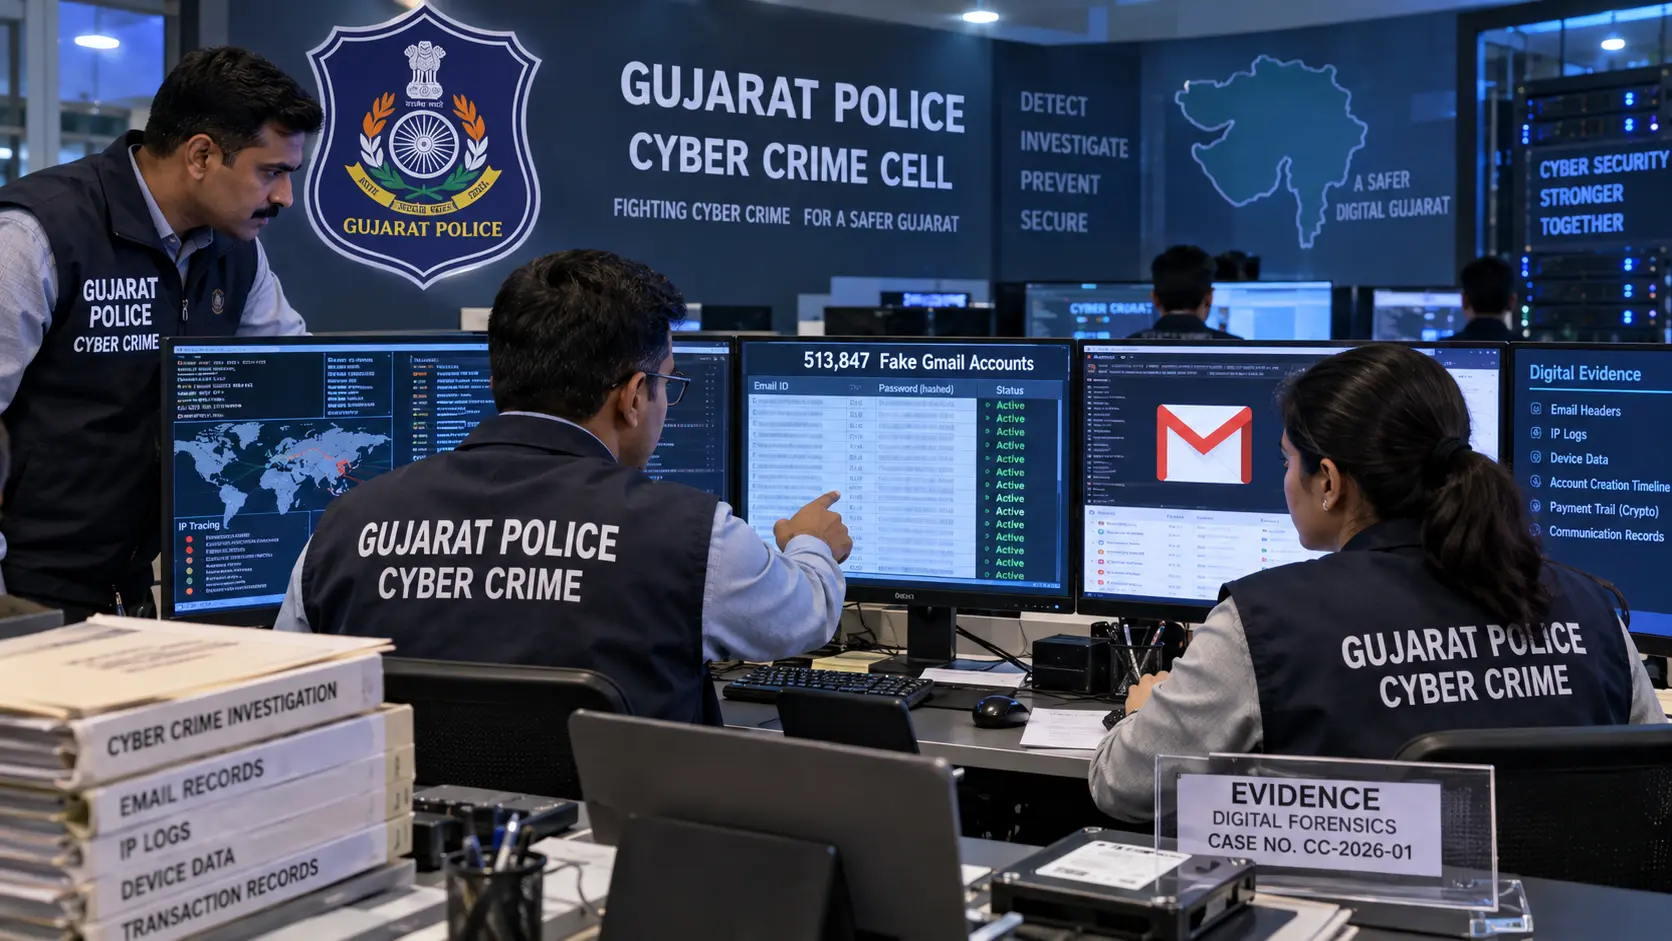
A major cybercrime investigation by the Gujarat Police Cyber Centre of Excellence has exposed a massive identity-as-a-service ring involving over 513,847 fake Gmail accounts. What began as a probe into a single bomb threat sent to government authorities on September 10, 2026, has quickly spiraled into one of the largest digital identity scams uncovered in the country.
The sheer scale of the operation has put Google’s account verification protocols under intense scrutiny. Investigators are currently working to determine how half a million accounts could be created, verified, and distributed across international borders without triggering automated anti-abuse algorithms.
How a Bomb Hoax Unraveled a Global Syndicate
The investigation gained momentum after a bomb threat email sent to Gujarat state officials turned out to be a hoax. Digital forensics teams traced the email back to a vast database containing login credentials for 513,847 Gmail accounts.
Rather than an isolated perpetrator acting alone, investigators found evidence of an organized bulk identity farm. The syndicate allegedly created and maintained these accounts for distribution to buyers, allowing criminals to rapidly rotate identities and evade law enforcement tracking.
Key Highlights of the Probe:
-
International Footprint: Investigators uncovered communication between suspects and buyers in Bangladesh, pointing to cross-border sales of identity batches.
-
Crypto Payments: Cryptocurrency transactions were allegedly used to anonymize payment flows between identity brokers and buyers.
-
Pre-Enabled Security: Many accounts had active two-factor authentication (2FA) configured, ensuring the criminal buyers maintained uninterrupted control over their purchased credentials.
The 2FA Paradox and Google’s Security Safeguards
Modern platforms deploy anti-detect mechanisms, device fingerprinting, and rate-limiting to prevent automated registration. However, the presence of 2FA on fake accounts highlights a crucial vulnerability: security measures designed to safeguard account owners can be weaponized by cybercriminals to preserve infrastructure.
| Operational Vector | Technical Method | Exploited Safeguard |
| Bulk Registration | Anti-detect browsers and residential proxies | Bypasses IP rate limits and device checks |
| Verification Bypass | Automated SMS-receiving farms | Circumvents single-phone registration caps |
| Identity Persistence | Pre-configured 2FA security settings | Prevents automated lockout by platform safety engines |
Gujarat Police are expected to formalize inquiries with Google to examine account creation logs, phone verification records, and IP cluster trends associated with the network.
Stay updated on technical policy and law enforcement developments on Matribhumi Samachar Technology & National News.
Frequently Asked Questions (FAQ)
Q1: Did Google suffer a direct security breach or data leak in this incident?
No. There is no evidence indicating that Google suffered a security breach or that a direct software vulnerability allowed this to happen. The investigation focuses on whether criminals exploited public sign-up and verification channels at scale.
Q2: What were the fake Gmail accounts used for?
While the investigation began due to a bomb-threat email sent to the Gujarat government, bulk email networks are commonly repurposed for phishing campaigns, financial fraud, spam distribution, and identity concealment.
Q3: How do cybercriminals set up 2FA on thousands of fake accounts?
Criminal networks typically use automated virtual phone services (SMS farms) or temporary SIM networks to complete phone verification steps during initial account registration.
Disclaimer
This article is compiled based on preliminary police reports, public statements by Gujarat Police officials, and ongoing investigative details as of September 2026. It is intended solely for informational and educational purposes. Further developments may emerge as law enforcement and technical teams continue their probe.